Related Topics:
Access Multiple Networks Managed-
Switch detects unauthorized network access
You can use encryption protocols such as SSH, HTTPS, or SNMPv3 to secure the switch's remote access, web interface, or network management, respectively. These unauthorized or malicious devices can infiltrate networks, compromise security, and jeopardize sensitive data. But what exactly is a rogue device, and why should businesses be concerned? Let's break down what rogue devices are, the potential threats they pose, and how to detect and prevent. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. It encompasses both hardware and software technologies, and it focuses on a variety of threats, working.
[PDF Version]
-
What to do if the fiber optic cable on the switch loses internet access
Experiencing a fiber outage can be frustrating, especially when you rely on internet services for work, entertainment, or communication. This guide will provide you with step-by-step troubleshooting tips to identify and potentially resolve common fiber internet issues. Fiber optic networks are celebrated for their speed and reliability, but even the best systems can encounter problems. This guide will walk you through diagnosing and resolving common. ■ How to quickly locate the problem when signal drops? When the internet gets slow or drops randomly, these tools help you track the issue fast: Focus on these spots: ■ How to fix issues quickly without long downtime? If a user suddenly loses connection, here's how to bring service back fast: Tip:. This document describes how to troubleshoot fiber optic interfaces by addressing some of the fiber optic module and cabling specifications. There are no specific requirements for this document.
[PDF Version]
-
What happens when two networks are connected to a single switch
When two networks share the same switch, there is a risk of data leakage or unauthorized access between networks. Switches operate at the data link layer (Layer 2) of the OSI model, examining incoming data packets and forwarding them to the intended recipient. Switches can be broadly. In my organization, we have 2 networks. A network for staff and another network for public Wi-Fi. For DNS I got a solution which works via search domains. The Issue now: What happens if network C or later network D needs to be. Where two directly connected PCs in different ip networks are able to ping each other if their network interfaces have their own ip address set as a gateway address too. Scenario 2 Where two or more Cisco switches are connected to a single common switch, each has a VLAN interface configured with a. Is it possible to do it, means sending 2 datas, TCP/IP and Internet on the same Ethernet networking via fiber optic and connect each RJ45 to his destination device. Are they really 2 different network.
[PDF Version]
-
Core switch connects to multiple network segments
A core switch is the backbone of a network, managing high-speed data traffic between multiple segments. It's designed to handle significant amounts of traffic with advanced features like redundancy and scalability. Primary Role: Acts as the central hub connecting distribution switches and routers.
[PDF Version]
-
Secondary distribution box with one switch for multiple lines
Secondary selective service achieves similar results by using switches on secondary voltages rather than primary voltages. With secondary selective service, each distribution transformer must be a.
[PDF Version]
-
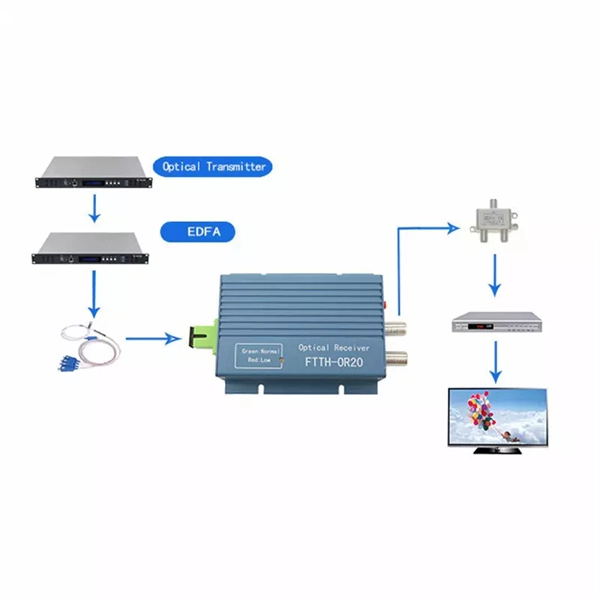
Aggregation Switch Access Layer 2
An aggregation switch operates at Layer 2 or Layer 3 of the OSI model, depending on the configuration and topology of the network. The controller uses protocols, such as Link Aggregation Control Protocol (LACP) or Static Link Aggregation, to combine physical links into a single. An aggregation switch is a network device that consolidates traffic from multiple access switches, wireless access points, or other edge devices and forwards it to core switches or routers. A Layer 2 access topology provides the following unique capabilities required in the data center: VLAN extension—The Layer 2 access topology provides the flexibility to extend VLANs between switches that are connected. An 8-port, Layer 2 switch made for 10G SFP+ connections. Faster replacement and priority support, covered for 5 years. High-performance 10G SFP modules for optimal connectivity. The aggregation (sometimes also called distribution) layer is a real crossroad. The two-tier design is well suited for small buildings with few wiring closets and access switches.
[PDF Version]
-
Does the access switch enable authentication-free access for its ports
1X authentication works by using an authenticator port access entity (the switch) to block ingress traffic from a supplicant (end device) at the port until the supplicant's credentials are presented and match on the authentication server (a RADIUS server). Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. Aruba ClearPass supports dynamic ACL-based and VLAN-based authorization. ACL-based authorization is classified into static ACL-based and dynamic ACL-based authorization. Imagine a situation where you have a public meeting room equipped with accessible Ethernet ports, and you want to. 802. Read this topic for more information.
[PDF Version]
-
OLT Access Switch
When you stream a 4K video, join a remote meeting, or play an online game on a gigabit fiber connection, an OLT silently coordinates all that data from your internet provider to your home. In short: The OLT (Optical Line Terminal) is the central control unit of a Passive Optical. OLT (Optical Line Terminal) and switches are critical devices in optical communication networks, but their optical modules differ significantly in types, functionalities, and applications. Let's discuss each one separately: 1. Application Scenario An apartment wants to use the XM60A to enable Omada equipment to access the OLT for networking and flexible deployment. They have the following demands in this example. 1) The switches. There are two important types of systems that make FTTH broadband connections possible. These are active optical networks (AON) and passive optical networks (PON). By far the majority of FTTH deployments in planning and in deployment use a PON in order to save on fiber costs.
[PDF Version]
-
Switch Layer 3 Access Layer
A Layer 3 switch (also called a multilayer switch) is a purpose-built hardware device that blends features of a traditional Layer 2 switch and a router. It plays a critical role in modern networks by performing high-speed packet forwarding while also making routing decisions at Layer. When planning an enterprise access network, one of the most common dilemmas is whether to deploy Layer 2 (L2) or Layer 3 (L3) switches. This. Layer 3 Switch vs. Router: What's the Difference? The OSI (Open Systems Interconnection) model is a conceptual framework that describes how network communication works across seven layers. Each layer handles a specific aspect of data transmission, and the layer at which a device operates defines. Layer 3 switches are advanced networking devices that combine the functions of both traditional switches and routers, offering enhanced capabilities for managing and directing data traffic across different network segments. this article will delve into the world of layer 3 switches, exploring their.
[PDF Version]
-
Access Switch Interface Table
This article describes how to create and delete switchboards in Access, and shows how to add and modify the items in a switchboard. End devices are the non-networking devices that connect to the network, such as IP phones, personal computers, wireless access points, printers, and IP cameras. Note: Access also provides a feature known as the Navigation Pane which you. Basically determine what each port is connected to, for the entire core and distribution layer of this network topology. Cisco NX-OS supports only IEEE 802. 1Q-type VLAN trunk encapsulation. This chapter describes the configuration of access or trunk ports on Cisco Nexus 5000 Series switches. It includes the following sections: Ethernet interfaces can be configured either as access ports or a trunk ports, as follows:. In Cisco Application Centric Infrastructure (ACI), interface configurations are performed by associating an interface policy group, which is a group of interface policies such as interface speed or link layer discovery protocol (LLDP), to an interface on a switch node.
[PDF Version]